From the Founder

Why I started this firm, and what I owe you.

EHR Resources has been doing one thing since 2011: helping healthcare organizations understand where their patient information is actually at risk, and what to do about it. Here is the thinking behind that, in my own words.

Thomas J. Johnson
Founder, President, and Principal Consultant
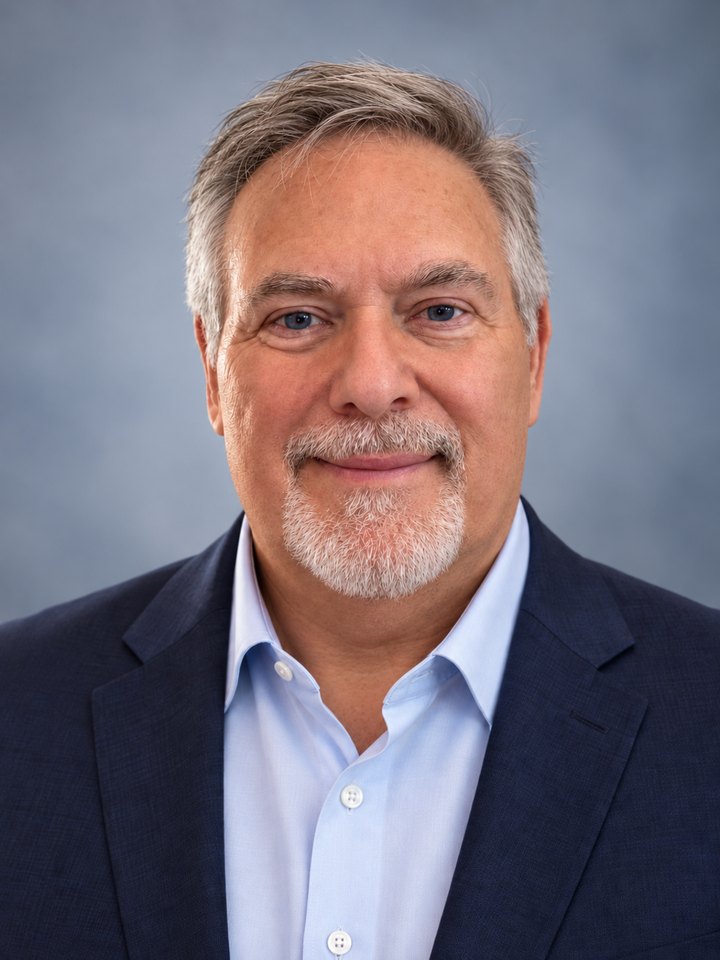
Thomas J. Johnson, founder and president of EHR Resources, LLC

Thomas J. Johnson · CPHIT, CPEHR, ITPM

Dear Colleague,

If you have landed on this page, there is a good chance you are weighing whether to hand an outside firm something uncomfortable: an honest look at how your organization protects patient information. I have been on the other side of that decision, and I know it is not a small one.

This firm exists because of a question I could not answer for three straight years.

Before EHR Resources, I worked under a State of Nebraska contract helping clinics, medical practices, and hospitals move from paper charts to electronic health records under the federal Meaningful Use incentive program. I worked alongside frontline clinicians, providers, and technical staff, and our teams were assigned more than 1,400 healthcare practices. That work is where this firm got its name.

One of the Meaningful Use measures required covered entities to conduct a HIPAA Security Risk Analysis. Our contract covered migration and attestation, not security assessments, so the same question came back from practice after practice: who actually does the risk analysis? Very few of them had anywhere good to send it. Around the same period I was selected to serve on a national working group of technical professionals drawn from 36 states, convened under the Department of Health and Human Services during Secretary Kathleen Sebelius's tenure, to help develop guidance for covered entities conducting their own internal security risk analyses.

Between the two, providers began calling me directly. They knew I understood the Privacy and Security Rules and had the technical depth behind it. In 2011 I started EHR Resources so I could answer that question properly, independently, and for anyone who asked.

A risk analysis is not a document you buy. It is a decision-making process you go through, and the document is simply the record of it.

The work has not changed much in character since. Conduct the analysis. Write policies and procedures that fit the organization rather than a template. Build a risk management plan someone can actually follow. Identify where compliance is genuinely exposed. Organizations in Nebraska, Kansas, Iowa, Colorado, Texas, California, and elsewhere have brought us in to do exactly that.

My background is not primarily in compliance. It is in technology. Across more than thirty years I have run IT operations in healthcare, insurance, and government, including roles as Director of Information Technology and interim CIO, with the focus always on data security, privacy, and protection. That matters more than it might sound. When I look at your environment, I am not reading a regulation and hunting for the paragraph that matches. I am looking at how your systems are actually configured, where the data actually moves, and who can actually reach it. Then I map that back to the Security Rule.

My first responsibility to a client is to tell the truth about what I find, including when the answer is inconvenient or when it is not what someone hoped to hear. A risk analysis that only produces good news is not doing its job. Neither is one so alarming that nobody can act on it. The value sits in between: a clear, prioritized, plainly written account of what is exposed, how much it matters, and what a reasonable next step looks like given your budget and your staffing.

I also want to be direct about what this work is not. No consultant can make an organization "HIPAA compliant," and anyone who tells you otherwise is selling something. Compliance is a posture you maintain, not a certificate you hang. What I can do is give you a defensible, well-documented analysis, a remediation plan you can actually execute, and evidence that your organization took its obligations seriously. If OCR, a payer, or a business partner ever asks how you arrived at your decisions, you will have an answer.

One more thing, and it is the part I care most about. When you engage this firm, you get me. Not a sales representative who hands you to an associate after the contract is signed. I do the interviews, I do the analysis, I write the report, and I am the one who picks up the phone six months later when a question comes up. That is a deliberate constraint on how fast this business grows, and I consider it worth every bit of the tradeoff.

The measure I pay attention to is not how many organizations we have worked with. It is how many keep asking us back. A good share of our engagements are with clients who return year after year, and that continuity is the part of this business I am proudest of.

If your last risk analysis was a template with your name typed into it, or if it has been a few years and the environment has changed underneath you, I would welcome a conversation. There is no charge for it, and no obligation on the other side.

Thank you for your time, and for the work you do.

Thomas J. Johnson

Thomas J. Johnson, CPHIT, CPEHR, ITPM
Founder, President, and Principal Consultant
EHR Resources, LLC · Veteran-Owned Small Business
Background

The experience behind the work.

Fourteen-plus years focused entirely on healthcare, built on three decades of technology leadership in regulated environments.

1,400+
Healthcare practices supported during the Nebraska EHR migration program
36 states
Represented on the national HHS working group developing internal SRA guidance
30+ years
IT leadership across healthcare, insurance, and government

United States Air Force veteran

EHR Resources is a federally verified Veteran-Owned Small Business through the SBA Veteran Small Business Certification program.

Senior technology leadership

Roles including Director of Information Technology and interim Chief Information Officer, with responsibility for infrastructure, security, and regulated data across multiple industries.

Fortune 500 and enterprise experience

Technology roles at two Fortune 500 insurance companies, bringing enterprise-grade security and governance practice to organizations that rarely get access to it.

Provider-side healthcare experience

Direct technology work inside a critical access hospital and a behavioral healthcare organization, so the realities of clinical workflow and thin IT staffing are familiar, not theoretical.

Deep command of the HIPAA rules

Working knowledge of the Privacy and Security Rules earned in practice, not from a manual, and applied across assessments, policy sets, and risk management plans since 2011.

Public sector and education

Technology roles in municipal government and a public school system, useful background for organizations navigating public funding, board oversight, and procurement requirements.

Built on recognized frameworks

Engagements are structured around NIST Special Publication 800-66 and 800-30, the guidance HHS itself points to for Security Rule risk analysis, with findings mapped to specific CFR citations.

Clients nationwide, relationships that last

Organizations served in Nebraska, Kansas, Iowa, Colorado, Texas, California, and beyond, a substantial share of them returning for engagements year after year.

What You Can Expect

Six commitments I make to every client.

These are not marketing lines. They are the operating rules of the practice, and you are welcome to hold me to them.

01

You work with the principal

The person who scopes your engagement is the person who conducts it and writes it. No handoff to junior staff after the signature.

02

Plain language, always

Reports are written so a board member, an office manager, and a systems administrator can each read the same document and know what to do.

03

Findings you can defend

Every finding ties to a specific regulatory citation or a stated best practice, with the distinction between the two made explicit rather than blurred.

04

Prioritized, not just listed

A hundred findings with no ranking is a burden, not a deliverable. You get a sequence, informed by real-world risk and what your organization can absorb.

05

Honest scope and honest pricing

Flat fees quoted up front. What is included and what would be billed separately is stated in writing before work begins, so there are no uncomfortable invoices.

06

We stay reachable

Questions after delivery are part of the engagement, not a new sales opportunity. The relationship does not end when the report is emailed.

Why Organizations Choose Us

The advantage of a specialist.

Large firms bring bench depth. Software vendors bring automation. Here is what a focused, principal-led practice brings that neither one does.

Healthcare is not a vertical to us

It is the entire practice. We are not applying a generic security methodology to a hospital. We understand clinical workflow, EHR platforms, and why a well-intentioned control that disrupts patient care will simply be worked around.

Technology depth, not just policy review

Thirty years of hands-on IT means the assessment goes past the binder. We look at how systems are configured and where data actually flows, not only at what the policy says should happen.

Right-sized for the organizations we serve

Critical access hospitals, independent practices, behavioral health providers, and business associates get senior attention at a scale and price that fits, instead of being the smallest account on a national firm's roster.

Continuity year over year

Clients who return are not re-explaining their environment to a new consultant each cycle. The institutional knowledge stays with the engagement, which makes each subsequent analysis sharper and faster.

Veteran-owned and accountable

A federally verified Veteran-Owned Small Business. For public-sector clients and health systems with supplier diversity goals, that status carries procurement weight in addition to what it says about how we operate.

Straight answers about risk

We do not sell fear and we do not sell false comfort. You get a measured read on your exposure, which is the only kind of read that supports a good decision.

Credentials & Affiliations

The background behind the signature.

CPHIT · Certified Professional in Health Information Technology CPEHR · Certified Professional in Electronic Health Records ITPM · State of Kansas IT Project Management Certification SBA · Verified Veteran-Owned Small Business HIMSS · Member, Nebraska Chapter U.S. Air Force · Veteran NIST SP 800-66 & 800-30 · Assessment methodology

EHR Resources, LLC is an independent advisory firm. We are not a government agency and we do not issue federal certifications. No consultant or vendor can certify an organization as HIPAA compliant.

Let's have the conversation.

A short, confidential call is the fastest way to find out where you stand and what a sensible next step would cost. No obligation, and you will speak with me directly.